N-able N-central Critical Vulnerabilities: What We Know So Far
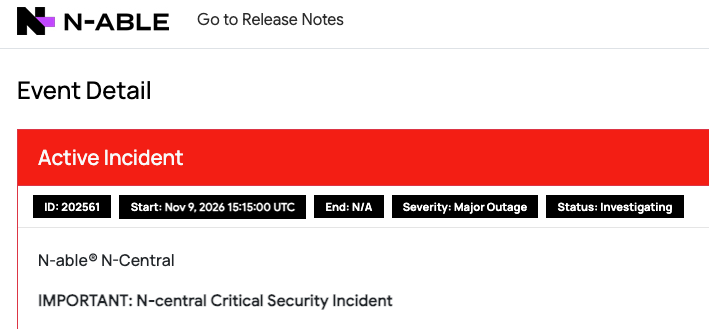
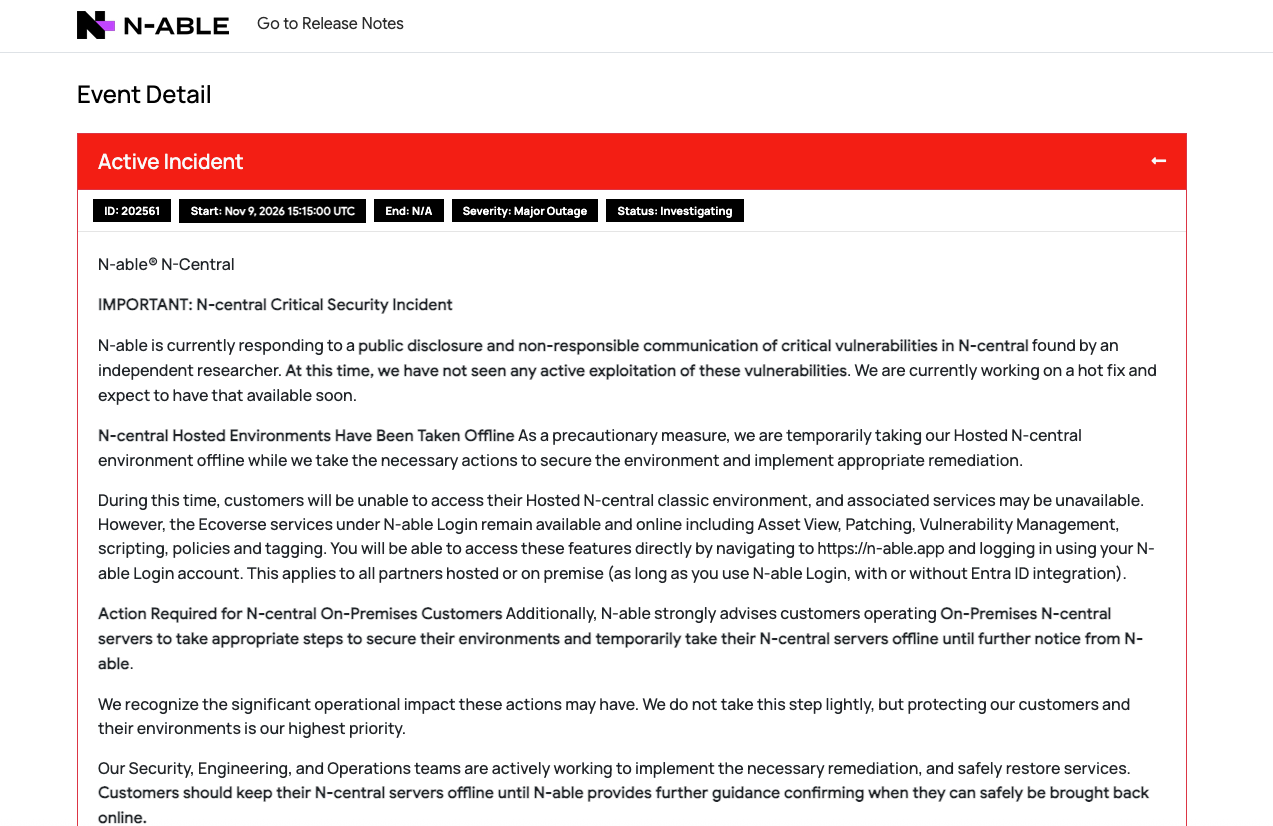
N-able has taken its hosted N-central classic environments offline following the public disclosure of critical vulnerabilities in N-central.
The company is also advising customers running on-premises N-central servers to take them offline until further notice while it works on remediation.
N-able says it has not seen active exploitation of the newly disclosed vulnerabilities at the time of its notice.
We’re monitoring the situation closely.
What Has Been Disclosed
The public research, published under the name Able2Shell, documents a number of vulnerabilities affecting N-able N-central.
One of the more serious chains starts without existing credentials and combines XML external entity processing with weaknesses in N-central’s internal session handling.
The published proof of concept demonstrates a chain capable of:
- Establishing an anonymous N-central MMS2 session
- Staging attacker-controlled XML content
- Triggering external entity processing during service import
- Accessing an internal NCI session
- Resetting an existing account password
- Authenticating using the attacker-selected password
- Writing and executing a JSP payload
- Executing operating-system commands as the
nableservice account - Optionally creating an enabled administrator account
The researcher reports successfully testing the chain against N-central Appliance 2026.4.0.31.
There is currently no publicly assigned CVE for this specific chain.
We are therefore tracking it internally as:
A Public Exploit Is Already Available
Importantly, this is not simply a vulnerability description.
A working public proof of concept has been released showing the full XXE-to-command-execution chain.
That materially changes the situation for defenders. Even where exploitation has not yet been observed, public exploit availability lowers the barrier for other researchers, scanners and eventually attackers to reproduce the technique.
At the time of writing, VULN-2026-0007 is not listed in CISA’s Known Exploited Vulnerabilities catalog.
That does not mean the vulnerability should be treated as low priority. N-able itself has taken the unusually strong step of taking hosted N-central environments offline and recommending that on-premises customers do the same.
What Previdian Is Seeing
So far, we have not seen any traffic targeting this specific exploit chain across Previdian’s honeypot network.
The existence of a public proof of concept does not mean exploitation is already occurring in the wild, and we do not currently have first-hand telemetry that would support making that claim.
We are actively monitoring for activity matching the disclosed techniques and will update the record if that changes.
Previdian Customers Have Been Notified
Previdian customers have already been notified about VULN-2026-0007.
Customer exposure has also been validated so teams can determine whether N-central is relevant to their own environment and prioritise action accordingly.
Right now we have:
- A critical vendor incident
- Hosted systems taken offline
- On-premises shutdown guidance
- Public technical disclosure
- Public exploit code
- No assigned CVE for this chain
- No CISA KEV entry
- No hits yet across Previdian’s honeypot network
Any one of those points may change quickly.
What Defenders Should Do
If you operate N-central on premises, follow N-able’s current guidance and keep the server offline until the company confirms that it can safely be returned to service.
Teams should also review their exposure, monitor for new N-able guidance and be prepared for CVE assignments or additional technical details as the incident develops.
We would not recommend waiting for a CVE assignment or CISA KEV entry before acting. The vendor’s own response already indicates how seriously it is treating the issue.
Track VULN-2026-0007
We’ll continue monitoring the disclosure, N-able’s remediation guidance, public exploit development and our own honeypot telemetry for evidence of exploitation.
You can follow the live Previdian record here:
https://previdian.com/VULN-2026-0007
If exploitation begins appearing in our sensors or credible new evidence becomes available, the record will be updated as the situation develops.